




Microsoft 365 Copilot Write, Update, Delete Actions Explained
Microsoft plans to let Microsoft 365 Copilot write, update, and delete data inside connected third-party apps, not just read it. Microsoft's September 22 Message Center entry lists the feature as "In development," with general availability targeted for October 2026, per the Microsoft 365 Message Center archive.
The change applies to Microsoft 365 Copilot's federated connectors, the MCP-type integrations that currently give Copilot Chat real-time read access to outside services, according to Microsoft's listing. That's a separate track from consumer Copilot, which runs under terms warning that "Copilot can make mistakes, and it may not work as intended" and isn't mentioned anywhere in this announcement.
The entry concerns organizations using Microsoft 365 Copilot and federated connectors, along with employees inside those tenants who rely on connected third-party apps. Consumer Copilot is covered by separate terms and isn't described here, so anyone using Copilot on a phone or personal Microsoft account has nothing to configure.
Microsoft has not listed the feature as generally available in the cited roadmap entry. It's marked "In development" with an October 2026 GA target. What follows separates what Microsoft has stated from what its own documentation leaves open, along with what admins can check before that target arrives.
What Microsoft 365 Copilot write, update, and delete actions will require
Microsoft documents both synced and federated connector models for Microsoft 365 Copilot. Synced connectors pull outside data into Microsoft Graph, where it's indexed alongside a tenant's own Microsoft 365 content, per Microsoft's extensibility documentation. The Message Center describes federated connectors differently, as giving Copilot Chat real-time read access to a third-party service, per the entry.
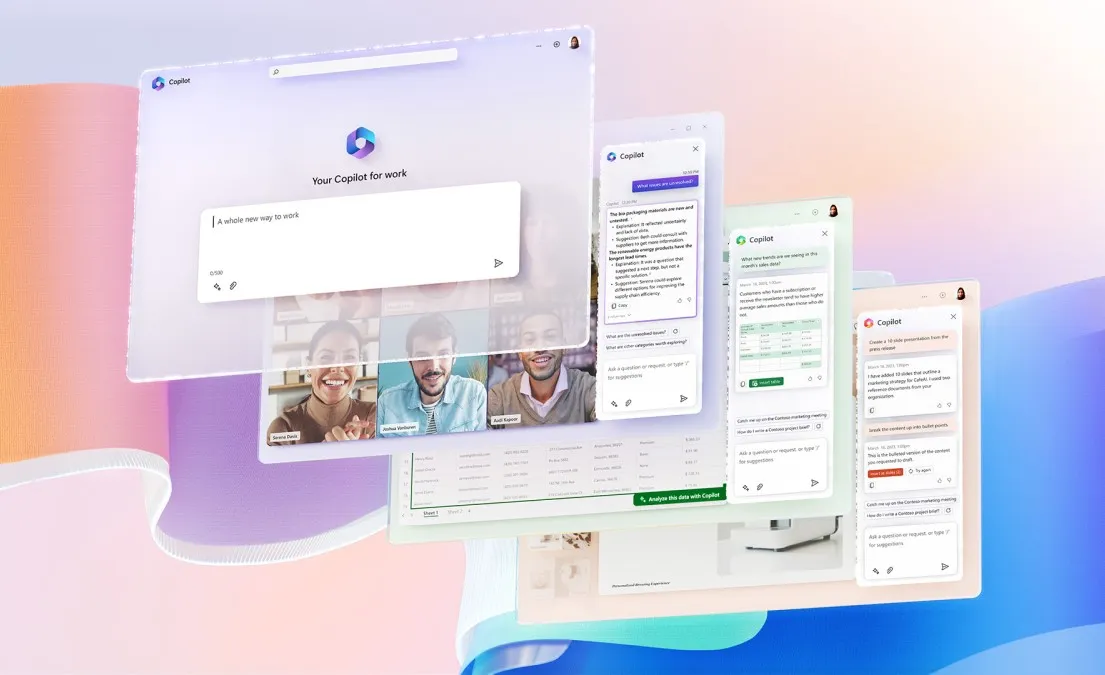
The planned update unblocks that federated pathway's write tools. Instead of only reading from a connected service, Copilot Chat would be able to create, update, and delete content directly in that outside system, Microsoft states. The goal, per the same listing, is letting users finish a task without leaving Copilot to handle it manually in the third-party app. In practical terms, it's Microsoft Copilot third-party app automation: the assistant acting on outside systems instead of only reporting what's inside them.
Microsoft has confirmed the core mechanics. Every create, update, or delete action requires a user's explicit confirmation before it runs, and Copilot is intended to act through the user's own account and existing permissions at the connected service, Microsoft says. Admins can already see which connectors have write and delete tools enabled and disable any connector that doesn't fit their organization's policy, per the same entry.
How Microsoft Copilot connector permissions and confirmation work
The stated safeguard is confirmation: nothing gets written, changed, or deleted without a person approving it first, according to Microsoft's announcement. But approval only proves someone clicked something. It doesn't prove Copilot found the right record, interpreted the request the way the user meant, or scoped the edit correctly.
A user having delete rights in a connected system, a CRM or ticketing tool, for example, says nothing about whether the AI picked the correct entry to act on. That's a different question from whether the person was allowed to make the change in the first place, and the cited announcement doesn't address it.
Microsoft's broader framing of Copilot supports that caution. The company describes Copilot as producing "useful drafts and summaries" for a person to review rather than fully automating a task, and its documentation states that "the responses that generative AI produces aren't guaranteed to be 100% factual," per Microsoft Learn guidance published last month. Write and delete actions raise the stakes of that same unreliability. A wrong draft is easy to fix; a wrong delete in a connected system may not be, depending on whether the target service keeps its own recovery options.
What Microsoft hasn't documented yet
Several operational questions aren't answered in the cited announcement or documentation. Microsoft hasn't named which third-party services get write support first, hasn't described how a connector's write capability gets reviewed before shipping, and hasn't said whether an undo or rollback option exists if Copilot edits or deletes the wrong record.
The confirmation screen itself is also unspecified. It's not stated whether a single approval covers one record or a batch, or whether a connector could execute a multi-record or irreversible change in one confirmed step.
Audit detail carries a similar gap. Microsoft's documentation says the level of detail captured in logs and reports "may vary depending on the service and configuration." Applied to a future write or delete action, reviewing a disputed change after the fact could provide an incomplete picture, depending on which third-party connector is involved and how it's set up. That's a documented limitation of the current audit system, not a claim about how this specific feature behaves once it ships.
What Microsoft 365 Copilot admin connector controls can do today
Admins already have some visibility into this system, separate from anything new tied to the write capability. Microsoft says admins can view each connector's read and write/delete tools in the Microsoft 365 admin center and disable any connector that doesn't meet their organization's policy, per the Message Center entry.
Microsoft has also published broader governance statements about Copilot agents generally, not this feature specifically. Agents operate within existing Microsoft 365 access boundaries and don't grant privileges beyond what a user is already authorized to access, and their activity stays subject to existing data loss prevention, retention, sensitivity-label, and compliance policies, according to Microsoft Learn documentation published in July. Nothing in that documentation confirms those protections have been separately verified for the federated-connector write and delete capability still in development.
Admins overseeing federated connectors can use the admin center now to inventory which connectors are currently enabled and which connected accounts carry broad edit or delete permissions in their target services, since that visibility already exists regardless of when the write tools ship. Microsoft hasn't announced which connectors get write support first, hasn't detailed how granular a single confirmation covers, and hasn't specified what audit trail a write or delete action will leave behind. The October 2026 target remains a roadmap date until Microsoft documents those specifics or admins can test them directly against a live rollout.
Comments
Be the first, drop a comment!