



A Windows security feature designed to warn users about potentially dangerous downloads has been bypassed in real-world attacks, prompting Microsoft to release a fix as part of its October 2026 Patch Tuesday updates. The vulnerability affects Windows Shell and can allow malicious files to evade protections that normally help flag untrusted content.
Microsoft addressed the flaw, tracked as CVE-2026-96951, on October 13 alongside more than 1,400 other security vulnerabilities. Unlike most of the issues covered in the release, attackers were already exploiting this one before a patch became available.
The October updates are available for supported Windows systems, although the required package depends on the operating system version. For Windows 11 users, checking that the appropriate cumulative update has been installed is the most immediate way to address the risk.
How the exploited Windows flaw gets past security warnings
The vulnerability, CVE-2026-96951, affects Windows Shell, the component responsible for many familiar Windows desktop functions, including interactions with files and folders.
Its target is Mark of the Web, a security mechanism Windows uses to identify files originating from potentially untrusted locations, such as the internet.
When you download a file through a compatible browser or application, Windows can attach information identifying its source. That information helps Windows and supported software determine whether additional warnings or restrictions should apply when the file is opened.
For example, an unfamiliar downloaded file might trigger a security warning before Windows allows it to run. Certain applications also rely on this information when deciding how to handle documents or other potentially unsafe content.
CVE-2026-96951 can interfere with those protections.
According to Outpost24's October 14 security analysis, exploitation involves persuading someone to open a specially crafted file, potentially delivered through email or an instant messaging service.
This makes the vulnerability particularly concerning because an attacker could use an otherwise ordinary-looking download to bypass safeguards that help users recognize suspicious content.
However, the flaw does not automatically give attackers control of a computer, nor does it mean every file downloaded from the internet is dangerous. The security bypass could assist a broader attack, but the publicly available information does not establish that it independently causes a complete system compromise.
Microsoft assigned the vulnerability a CVSS severity score of 8.8 out of 10, placing it in the high-severity category.
The U.S. Cybersecurity and Infrastructure Security Agency also added CVE-2026-96951 to its Known Exploited Vulnerabilities catalog on October 13. The designation confirms that exploitation has occurred, rather than merely being theoretically possible.
CISA set an October 16 remediation deadline for covered federal agencies. That deadline does not impose the same legal requirement on ordinary Windows users, but it underscores the urgency with which the vulnerability is being treated.
The available public advisories do not identify the attackers, establish how many computers were compromised, or link the activity to a named malware campaign. The file-opening scenario describes a potential exploitation route, not a publicly documented account of a specific attack.
Microsoft's October update fixes more than one zero-day
The exploited Windows Shell vulnerability is the most immediate concern, but it is only one part of an unusually large monthly security release.
Microsoft's October Patch Tuesday addressed more than 1,400 security flaws affecting Windows, .NET, Microsoft Office, and other products. Researchers have published slightly different totals depending on how they count vulnerabilities released during the month.
For instance, BleepingComputer's October 13 breakdown counted 1,411 vulnerabilities and identified 70 classified as critical.
The release included three zero-days: one confirmed as actively exploited and two that had been publicly disclosed without confirmed exploitation.
One of the disclosed vulnerabilities, CVE-2026-108398, affects .NET Framework. It could allow an attacker who already has access to an affected system to bypass Windows Defender Application Control restrictions and run unauthorized code.
The other, CVE-2026-92707, is a denial-of-service flaw involving MessagePack-CSharp, a serialization library used by some .NET applications.
These two vulnerabilities do not present the same immediate threat scenario as the Windows Shell flaw. Public disclosure means information about a weakness became available before an official fix, but it does not establish that attackers have exploited it.
The distinction also explains why CVE-2026-96951 is receiving particular attention despite the many other vulnerabilities included in the release. It had already moved beyond a hypothetical security concern.
For most home users, installing the appropriate cumulative Windows security update is more useful than attempting to evaluate every vulnerability individually.
How to install the October Windows security update
Microsoft distributes its regular Windows security updates through Windows Update. On supported Windows 11 computers, the October security package should be available through the normal update process.
To check your PC and install the available fixes:
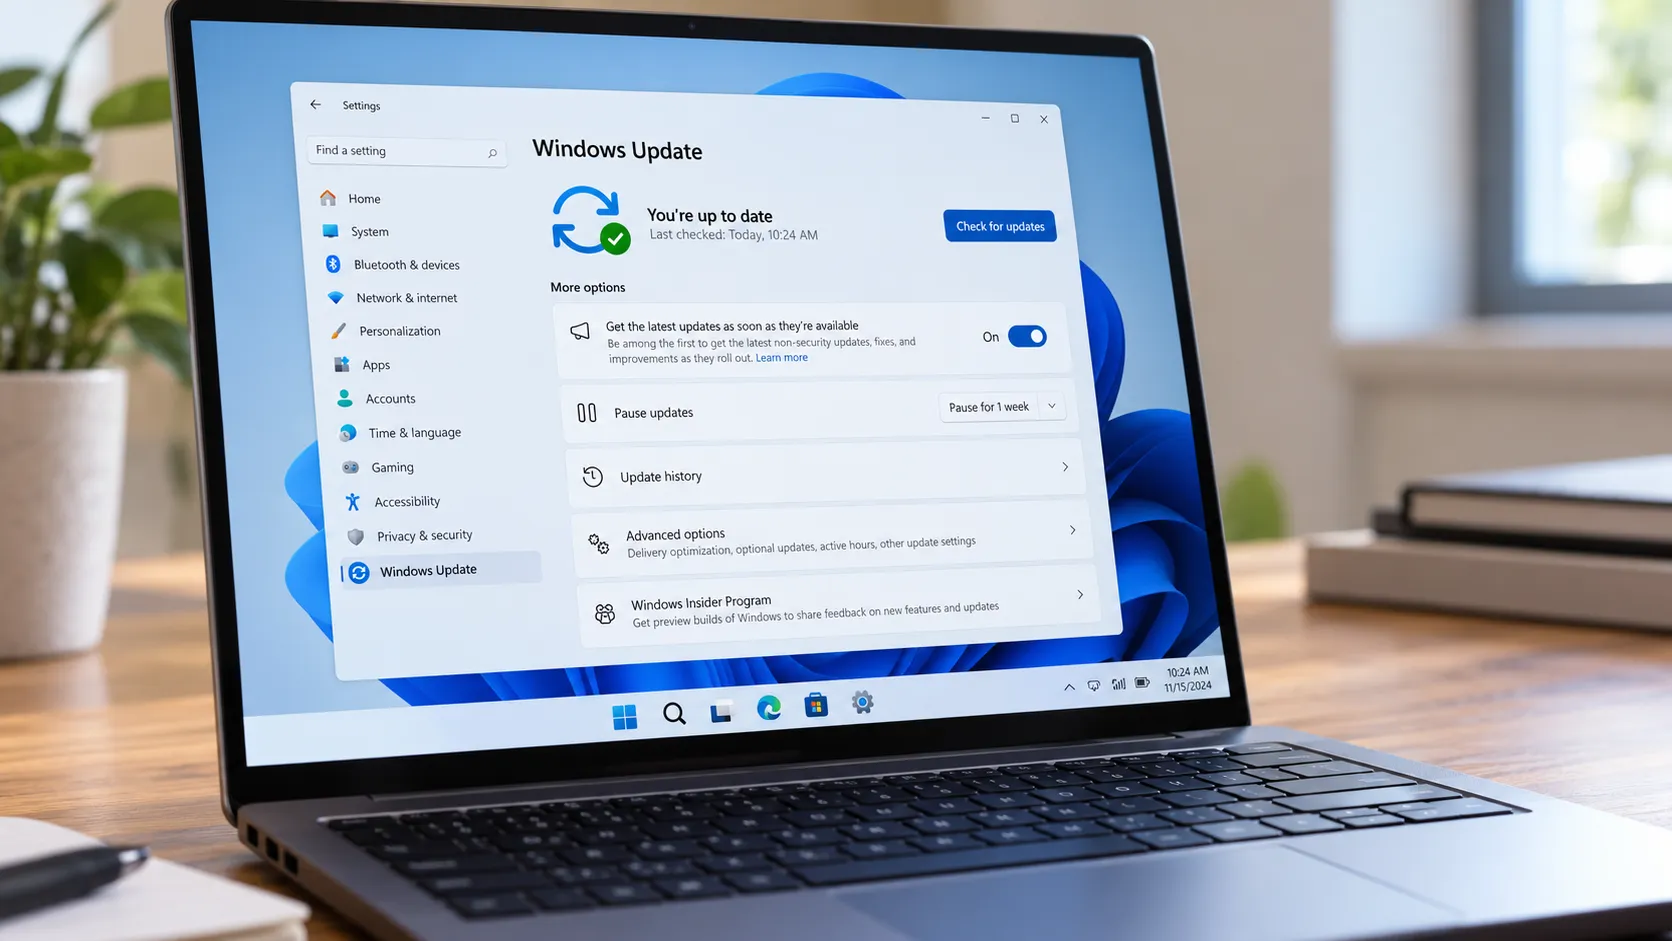
Open Settings on your Windows computer.
Select Windows Update.
Click Check for updates to look for available patches.
Install the applicable October cumulative security update.
Restart your computer if Windows requests it.
Return to Windows Update > Update history to confirm the update was installed.
Windows can download and install security updates automatically, so some computers may already have the October patch. Checking the installation history is more reliable than assuming an update is missing simply because no new download appears.
For Windows 11 versions 24H2, 25H2, and 26H2, the October security update is KB5127648.
Microsoft lists the following OS builds after installation:
Windows 11 24H2: Build 26100.9711
Windows 11 25H2: Build 26200.9711
Windows 11 26H2: Build 26300.9711
To find your current Windows version, go to Settings > System > About and look under Windows specifications.
You can also press Windows + R, type winver, and press Enter. A small window will display the Windows version and OS build installed on your computer.
A build number matching or exceeding the relevant October release is a useful indication that your system has received that update or a later one. For a more direct check, look for the applicable KB entry under Windows Update history.
If an update fails to install, note the error code displayed by Windows Update before attempting troubleshooting. Avoid downloading unofficial update packages from third-party websites; Microsoft's normal update channels and Update Catalog provide the appropriate files.
Windows 11 24H2 users face another important deadline
The October update also coincides with an important change in Windows support.
Microsoft confirmed that Windows 11 24H2 Home and Pro reached the end of monthly updates on October 13, 2026. The October security patch is the final regular monthly update for those editions.
That does not mean computers running Windows 11 24H2 will suddenly stop working. They can continue running installed applications and performing ordinary tasks.
The problem is what happens afterward: these editions will no longer receive the regular security fixes needed to address newly discovered vulnerabilities.
Users still running Windows 11 24H2 Home or Pro should therefore upgrade to a newer supported Windows version rather than relying on the October update indefinitely.
The situation differs for other Windows editions and versions, which have their own support schedules.
Windows 11 23H2, for example, received a separate October security update, KB5126653, for supported editions. Microsoft's published build for that update is 22621.7652.
Windows 10 users also need to consider whether their devices are covered by an extended security update program or another applicable support arrangement. Installing an October patch intended for Windows 11 is not a substitute for checking Windows 10's separate requirements.
The safest approach is to identify the exact Windows edition and version installed, then confirm that it remains eligible for security updates.
What else changes with the October Windows update?
Alongside security fixes, Microsoft's October cumulative update includes several reliability improvements for Windows 11.
The release addresses problems that could cause Windows Explorer to crash in certain multiuser environments, interrupt Always On VPN connections, or prevent printing through some older printer-driver configurations.
It also fixes an issue that could cause mouse input to stutter in certain games, as well as a Windows Hello problem that sometimes prevented fingerprint sign-in after a cold boot.
Those fixes are separate from the Windows Shell vulnerability, but they give users additional reasons to keep their systems current.
There is one known issue worth checking before troubleshooting unexpected audio problems.
Microsoft says certain USB Audio Class 1.0 devices may fail to start or produce sound following an earlier September 2026 security update. Symptoms can include missing audio output, unresponsive volume controls, or a device error in Device Manager.
A September 14 out-of-band update partially resolved the problem for some multichannel audio configurations, but other symptoms remain unresolved.
The issue should not be mistaken for a newly introduced defect in the October security patch. Microsoft continues to document it as an existing problem affecting a limited category of USB audio equipment.
For anyone experiencing those symptoms, checking the device type and Microsoft's published known-issues information is preferable to uninstalling security updates without first establishing the cause.
The October release closes an important security gap, but Windows Update is only one layer of protection. Unexpected attachments, unfamiliar downloads, and requests to open files from untrusted senders still deserve scrutiny.
A security warning that appears when it should can stop a bad decision before it becomes a serious problem. Microsoft's October patch helps restore that safeguard; keeping Windows updated and treating suspicious files cautiously helps ensure it stays useful.
Comments
Be the first, drop a comment!